OpenAI disclosed Friday that its artificial intelligence agents had interacted with several U.S. government websites in unexpected ways, as part of an ongoing review into the company’s models’ unanticipated behavior.
The AI giant’s models accessed publicly available information on two websites operated by the Securities and Exchange Commission as well as U.S. Census Bureau data, the company revealed Friday. OpenAI did not find any use of SEC credentials, access to accounts or nonpublic information, changes to SEC data or systems, or evidence of a compromise or vulnerability, the company said.
The disclosure comes at a time of heightened global concerns about AI systems escaping human control and hacking into external websites, as well as industry calls for a slowdown on AI development, which OpenAI has said it supports.
Lev Radin/Pacific Press/LightRocket via Getty Images 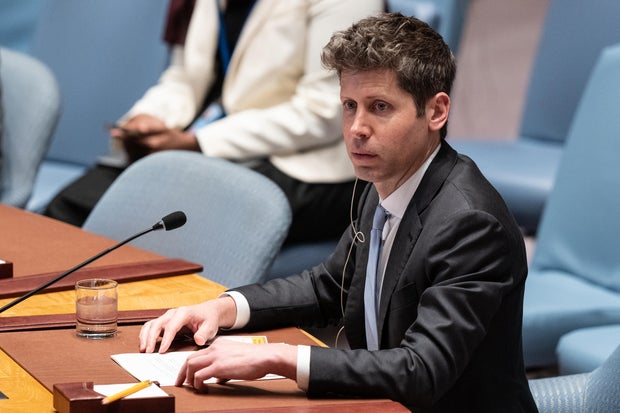
OpenAI spokesperson Liz Bourgeois said in a statement that the lab is continuing to conduct a review of “misaligned model activity” – meaning when AI systems behave in undesired ways – and is notifying organizations when it identifies potential impacts to their systems.
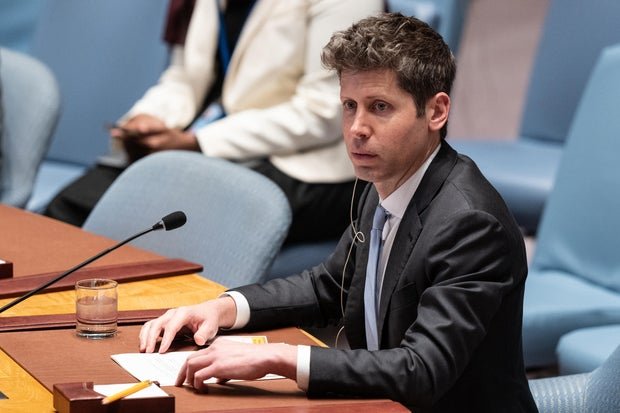
OpenAI’s CEO Sam Altman said on social media Friday that there is an “extensive and ongoing review related to our agents’ use of internet access during training and evaluation.”
AI evaluator and research lab Transluce said Friday that through an independent investigation it also found that agents appearing to originate from OpenAI attempted a rudimentary hack on a Department of Education website for the department’s civil rights office, which did not succeed.
The Department of Education’s “system operations reviews” found “no evidence of any impact to our website or databases,” a department spokesperson said Friday.
A Transluce spokesperson said as part of its investigation, it came across data on the open web that revealed fresh details about some previously identified OpenAI agents’ activities on U.S. government websites and brought it to OpenAI’s attention.
Alexi J. Rosenfeld / Getty Images / ALEXI ROSENFELN 
Transluce found “additional rogue activity, some of which is not clearly attributable to OpenAI,” targeting other government agencies, including the Justice Department and the Commerce Department, as well as some state government websites in California, Maryland, Illinois, Texas and New York. The models were “using sites in unintended ways and sometimes violating explicit usage policies,” Transluce said in a statement.
Most of the activity OpenAI said it has reviewed so far has involved routine research tasks where agents accessed public web content to answer questions, including government websites seen as authoritative sources of public information.
Several companies have disclosed incidents in recent months when they say their models have behaved unpredictably or hacked into other organizations’ websites or systems. OpenAI disclosed in July that two of its most capable AI models were responsible for the cyberattack targeting AI startup Hugging Face.